You are using an out of date browser. It may not display this or other websites correctly.
You should upgrade or use an alternative browser.
You should upgrade or use an alternative browser.
Security Advisory / Vulns / 0day
- Thread starter old.Osy
- Start date

old.Osy
No longer scrounging, still a bastard.
- Joined
- Dec 22, 2003
- Messages
- 2,759
- Thread starter
- #152
To whoever is born before the 80's - High-severity WinRAR 0-day exploited for weeks by 2 groups

- Joined
- Dec 22, 2003
- Messages
- 12,581
Poor WinRAR, first it's nobody ever registering, it's now a security vulnerabilityTo whoever is born before the 80's - High-severity WinRAR 0-day exploited for weeks by 2 groups
old.Osy
No longer scrounging, still a bastard.
- Joined
- Dec 22, 2003
- Messages
- 2,759
- Thread starter
- #154
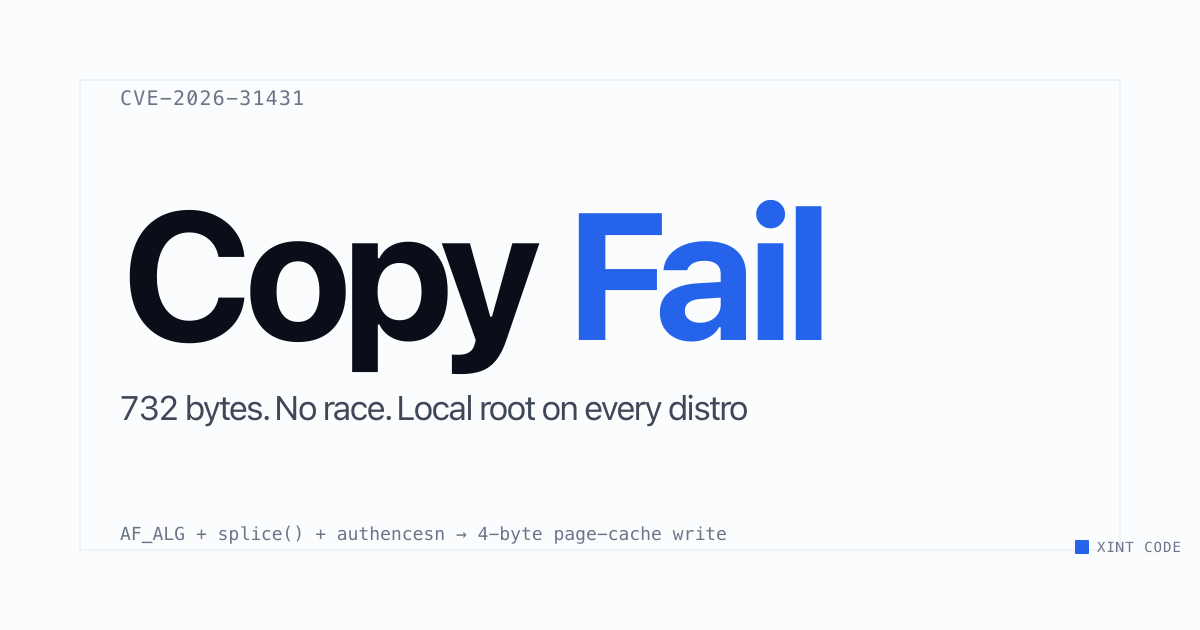
Copy Fail — 732 Bytes to Root
CVE-2026-31431. 100% Reliable Linux LPE — no race, no per-distro offsets, page-cache write that bypasses on-disk file-integrity tools and crosses containers. Found by Xint Code.
 copy.fail
old.Osy
No longer scrounging, still a bastard.
- Joined
- Dec 22, 2003
- Messages
- 2,759
- Thread starter
- #155

Popular DAEMON Tools software compromised
Targeted by threat actors: individuals and organizations across 100+ countries and territories, with the majority of victims located in Russia, Brazil, Turkey, Spain, Germany, France, Italy, and China.
 securelist.com
old.Osy
No longer scrounging, still a bastard.
- Joined
- Dec 22, 2003
- Messages
- 2,759
- Thread starter
- #156

LastPass says hackers stole customer data through a supply chain breach at Klue
LastPass notified customers that personal data and support cases were stolen after hackers breached Klue and used stolen OAuth tokens to access Salesforce.
 thenextweb.com

- Joined
- Dec 11, 1997
- Messages
- 9,077,799
This is the biggest issue facing any Company, you are only secure as your weakest link in the chain. Do not assume anything outside of your Company unless verified by security auditors to a well publicised standard.

Zarjazz
Identifies as a horologist.
- Joined
- Dec 11, 2003
- Messages
- 2,490
Pretty much every site running PHP is scrambling to apply this security fix, it's a bad one: PHP: News Archive - 2026
@Deebs get patching!
@Deebs get patching!
Last edited:
- Joined
- Dec 11, 1997
- Messages
- 9,077,799
I did it the moment I received the alert, also got a phone call from a nephew advising me about the vulnerability. He reads FH.Pretty much every site running PHP is scrambling to apply this security fix, it's a bad one: PHP: News Archive - 2026
@Deebs get patching!
Lots of sites took themselves offline due to the complexity of patching or upgrading the php version, still lots of sites dark even now.
Users who are viewing this thread
Total: 2 (members: 0, guests: 2)